Published: September 10, 2026 Author: Tech & Security Desk
Main Facts
Switching between password management applications on mobile devices has historically been a cumbersome chore, often requiring users to export vulnerable plain-text files, manage local directory paths, and manually reconfigure advanced credentials. Google is fundamentally rewriting this user experience.
The tech giant has officially introduced a streamlined, native password manager switching mechanism built directly into the Android operating system. Moving forward, Android users will no longer need to rely on legacy CSV (Comma-Separated Values) files to migrate sensitive login credentials when transitioning from one credential provider to another.
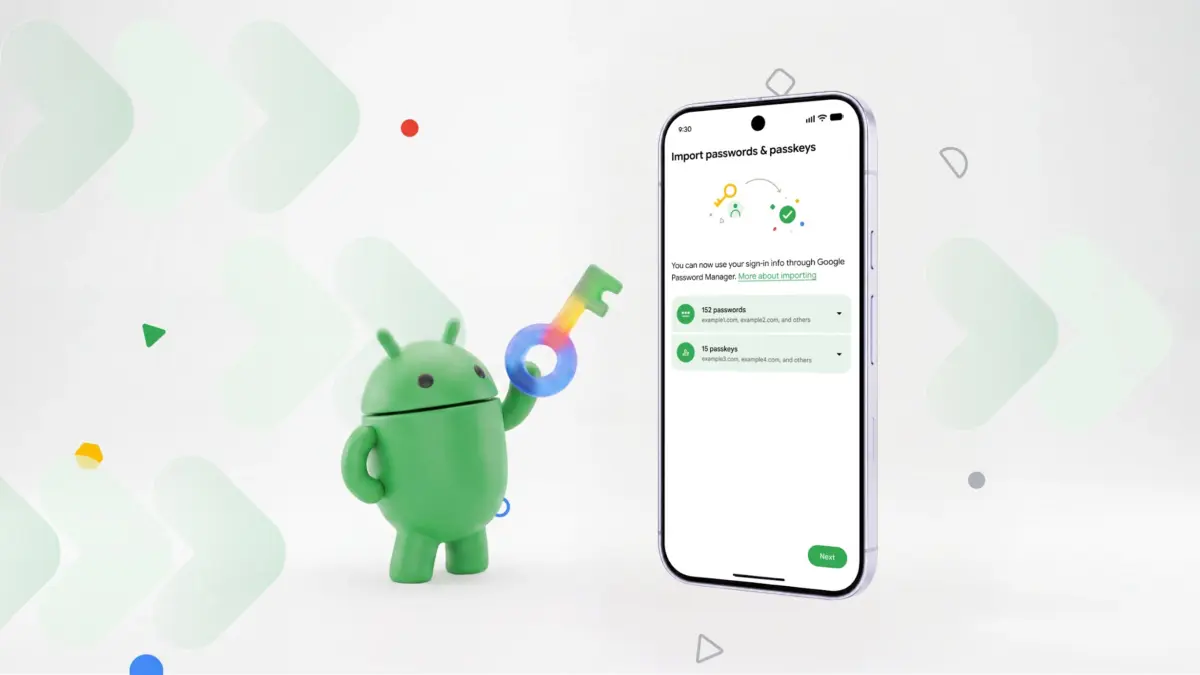
Instead, the new framework allows users to transfer entire vaults—including traditional passwords and modern, highly secure passkeys—directly between apps through an automated, secure pipeline. Major industry players, including 1Password, Bitwarden, and Dashlane, have already partnered with Google to support the initiative, alongside Google’s own native Password Manager.
Designed with backwards compatibility in mind, the feature rolls out to all devices running Android 8.0 Oreo or higher, instantly impacting billions of active mobile users worldwide. By automating app-to-app data handoffs, Google aims to eliminate the friction that discourages users from adopting better security tools, while simultaneously closing a critical vector for accidental data exposure.
Chronology of Password Migration and the Road to Android Integration
The Era of Manual Exports (Pre-2024)
For over a decade, migrating passwords between different software ecosystems was treated as an afterthought by major operating system developers. If a user wished to switch from a browser-integrated tool to a dedicated third-party vault—or jump between competing password managers—they were forced to navigate a precarious routine.
This legacy workflow required users to log into their existing manager, dig deep into desktop settings, and export an unencrypted or loosely encrypted CSV file containing every single username and password they owned. This file had to be downloaded locally onto the device’s storage, manually uploaded to the destination app, and subsequently deleted by the user.
Security experts repeatedly flagged this process as a severe vulnerability. If a user failed to securely wipe the downloaded CSV file, malicious applications or casual device snoopers could easily access plaintext credentials. Furthermore, as the industry began transitioning away from passwords toward passkeys—cryptographic credential tokens tied to specific hardware and software environments—CSV exports became entirely obsolete, as traditional file formats could not properly handle complex private-key structures.
The Rise of Credential Provider APIs
Recognizing the limitations of fragmented security storage, platform developers began laying the groundwork for standardized credential management. Google’s introduction of the Credential Manager API in recent Android iterations unified sign-in methods, making it easier for apps to handle passkeys, federated sign-ins (like "Sign in with Google"), and passwords under one unified umbrella.
However, migration remained a glaring weak spot. While operating systems could safely store and retrieve credentials for daily use, moving an entire database from App A to App B still relied on proprietary, clunky import tools or custom scripts.
The September 2026 Breakthrough
On September 10, 2026, Google bridged the final gap in mobile credential mobility. By implementing a direct inter-app communication protocol at the operating system level, Android effectively turned password migration into a native service. Rather than forcing applications to build custom parsers for external file formats, Android acts as a secure, neutral mediator that oversees the direct, encrypted transfer of data blocks from one verified password provider to another.
Supporting Data and Technical Architecture
To understand why this development is a watershed moment for mobile security, one must examine the technical mechanics of how data moves under the new Android framework.
How the New Migration Pipeline Works
Initiation: The user opens their newly installed or preferred password manager app and navigates to the settings menu to select the "Import" or "Switch from another app" option.
Discovery & Coordination: Android queries the system to detect other password manager apps currently installed on the device that support the new migration protocol.
Secure Handshake: Once the source app is selected, the operating system establishes a secure, sandboxed communication channel between the two applications, bypassing external device storage entirely.
User Verification & Biometric Gate: Before any data changes hands, the user is presented with a clear summary screen detailing what is about to be transferred. Authorization requires a biometric confirmation (such as a fingerprint or facial scan) or device PIN.
Execution: The source app packages the database—including encrypted metadata and passkeys—and transmits it directly across the system-managed channel to the destination app, which instantly ingests and indexes the records.
The Passkey Factor
One of the most significant technical achievements of Google’s new system is its native handling of passkeys. Unlike standard alphanumeric passwords, which are simply strings of text, passkeys consist of a public-private key pair. The private key remains securely stored on the user’s device and is designed never to leave it unprotected.
Under the old CSV-based regime, transferring passkeys was practically impossible because file-based exports lacked the standardized schema to safely move cryptographic keys without breaking their association with origin domains. Google’s new framework utilizes secure operating system hooks to safely migrate passkey associations, ensuring that users do not have to re-register their accounts with hundreds of websites when switching providers.
Device Compatibility and Adoption Reach
Google has engineered the feature for maximum inclusivity. By extending support down to Android 8 (Oreo), the company ensures that the vast majority of active Android smartphones and tablets—representing well over two billion devices globally—can take advantage of the seamless migration tool.
At launch, the ecosystem boasts heavy hitters from the password management industry:
1Password: Long regarded as an enterprise and consumer favorite for security.
Bitwarden: The leading open-source password management solution.
Dashlane: Known for its user-friendly interface and proactive security audits.
Industry analysts expect smaller independent password providers to adopt the open Android framework in the coming months, standardizing the migration process across the entire mobile landscape.
Official Responses and Industry Reactions
The announcement has been met with widespread applause from cybersecurity advocates, privacy watchdogs, and competing software developers alike.
A spokesperson for Bitwarden highlighted the reduction of user friction:
"For years, our support teams spent significant time walking less-technical users through the perilous process of exporting, securing, and deleting CSV files. By partnering with Google to build an automated, system-level transfer protocol, we are removing the single biggest psychological barrier that keeps people stuck using inferior, built-in browser tools instead of dedicated, highly secure password vaults."
1Password engineering leads emphasized the win for next-generation security:
"Passkeys are the future of authentication, but their adoption relies heavily on how easily users can manage them. If moving between providers meant losing your passkeys, users would hesitate to switch. Google’s new framework preserves the integrity of cryptographic credentials during migration, ensuring that better security does not come at the cost of user convenience."
From Google’s perspective, the feature aligns with the company’s broader push toward a passwordless future and enhanced mobile safety. In an official statement accompanying the release, Google reiterated its commitment to making secure digital hygiene as frictionless as possible.
"Security shouldn’t feel like a chore, and switching to a better tool shouldn’t require cybersecurity expertise," a Google product manager noted. "By eliminating CSV files, we are not only making the transition smoother—we are closing a notorious loophole that has compromised user data for decades."
Implications for Users, Competitors, and the Security Landscape
The rollout of this native password manager switching mechanism carries profound implications for the digital security ecosystem, consumer habits, and the competitive dynamics of the software market.
1. Drastic Reduction in Accidental Data Exposure
The most immediate beneficiary of this update is everyday cybersecurity. Human error remains the weakest link in digital defense. When users were forced to export CSV files, common mistakes included:
Leaving the CSV file in the phone’s public Downloads folder indefinitely.
Accidentally syncing the unencrypted file to cloud storage services (like Google Drive or Dropbox) where it could be indexed or exposed via misconfigured permissions.
Forgetting to empty the device’s trash bin after the migration was complete.
By completely eliminating the file-export step and conducting transfers via encrypted, memory-to-memory operating system channels, this entire class of user error is eradicated.
2. Heightened Market Competition
In the past, password managers enjoyed a degree of "vendor lock-in" simply because the migration process was too intimidating for the average consumer. If a user grew dissatisfied with a particular app’s pricing, interface, or feature set, the inertia of dealing with CSV exports often kept them from switching.
With a few taps and a biometric scan, users can now migrate their entire digital life to a competing service in seconds. This newfound fluidity is expected to increase market competition, forcing password manager companies to continuously innovate, improve user interfaces, and offer competitive pricing to retain their subscriber bases.
3. Accelerated Passkey Adoption
As web services increasingly transition to passkeys, consumers have expressed anxiety about being locked into a single ecosystem. If a user’s passkeys are trapped inside one specific app with no clean way to export them, they may be reluctant to adopt passkeys in the first place.
By proving that passkeys can be securely and portably migrated between independent applications via Android’s framework, Google has provided a blueprint that may soon be adopted by other operating system vendors, such as Apple. This interoperability is a crucial milestone for achieving widespread, mainstream acceptance of passkey technology.
What’s Next?
As Android 8+ users begin seeing the feature roll out through Google Play Services and partner app updates, attention will inevitably turn to rival platforms. Industry watchers are already questioning whether Apple will introduce a comparable, file-free migration pipeline for iOS users in upcoming software cycles.
For now, Android users stand at the forefront of a safer, more flexible digital era—one where managing your digital identity is no longer bound by outdated files, but empowered by smart, secure system architecture.