
If anything has been made unequivocally clear by the events of 2026, it is that cybersecurity is no longer a background concern, an IT footnote, or a line item delegated to mid-level management. Today, digital security occupies the front and center of geopolitics, commerce, and daily life, woven inexorably into nearly every major news story of the year.
As the world grapples with persistent socioeconomic inequalities, a worsening climate crisis, and the perennial shadow of global health threats, a turbulent digital current runs beneath it all. Wars are no longer fought solely on physical battlefields; they are contested in real-time across digital networks. Governments increasingly weaponize citizens’ data against them, sophisticated botnets quietly undermine democratic institutions, nation-state actors target civilian infrastructure ranging from power grids to municipal water systems, and brazen ransomware gangs hold critical institutions hostage for multi-million-dollar payouts.
The attacks are bolder, more destructive, and increasingly difficult to contain. As we cross into the closing quarter of what has become a watershed year for digital assaults and hybrid warfare, an examination of the worst breaches reveals not just a series of isolated failures, but a systemic unraveling of the modern digital trust architecture.
Main Facts: The 2026 Threat Landscape
The cybersecurity crises of 2026 share common threads: systemic vulnerabilities, aggressive state-sponsored proxy warfare, third-party vendor blind spots, and an over-reliance on digital identity infrastructure that has itself become a liability.

The year has been defined by unprecedented targets: federal oversight agencies, core open-source software supply chains, critical utility grids, social media algorithmic loopholes, and massive repositories of biometric and government-issued identification.
- The Federal Government Breached: From internal political overhauls at the Social Security Administration to high-level espionage targeting the FBI and ATF, government agencies have proven remarkably porous.
- Critical Infrastructure Under Siege: European energy grids and over a hundred U.S. water treatment facilities have faced direct hostile incursions by state-backed actors.
- The Software Supply Chain Collapse: Widespread open-source ecosystem compromise has allowed malicious code to cascade down into platforms operated by tech giants like OpenAI and Vercel.
- Identity Infrastructure Compromise: The exposure of hundreds of millions of passports and driver’s licenses has effectively crippled the foundational assumptions of modern "Know Your Customer" (KYC) compliance and digital age verification.
Chronology: A Year of Relentless Escalation
The trajectory of 2026’s cyber catastrophes unfolded in rapid, compounding succession across the calendar year:
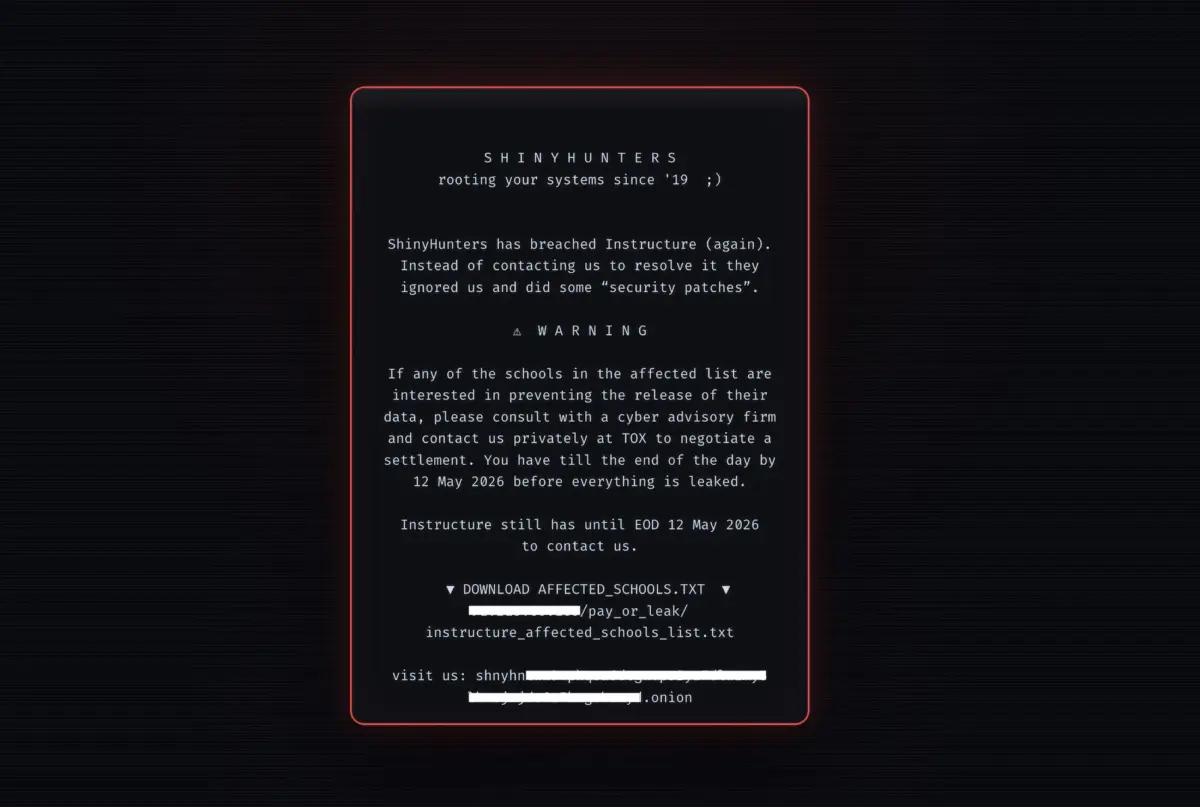
- Early 2026: Meta’s AI chatbot emerges as an unintentional accomplice, exploited by bad actors to hijack tens of thousands of high-profile Instagram accounts simply by asking the system to route password reset links to attacker-controlled emails. Meanwhile, the ShinyHunters gang ramps up voice-phishing campaigns, culminating in the breach of educational tech giant Instructure (Canvas).
- March 2026: Medical technology giant Stryker is targeted by pro-Iranian hacktivist group Handala, which remotely wipes tens of thousands of employee devices, severely disrupting operations. Simultaneously, software supply chain attacks compromise critical tools like Aqua Security’s Trivy scanner and Bitwarden. Toymaker Hasbro is forced offline by a devastating cyberattack, halting business operations for weeks.
- April 2026: The FBI officially declares a "major cyber incident" after unclassified surveillance systems containing sensitive wiretap data and target phone numbers are compromised by suspected Chinese state-backed actors. Web hosting firm Vercel also discloses customer data theft stemming from upstream supply chain compromises.
- May 2026: Following a ransom refusal, ShinyHunters strikes back at Instructure by defacing Canvas login pages during U.S. school finals, disrupting national examinations. OpenAI discloses a minor data leak tied to code security issues.
- June 2026: Market research firm Klue suffers a massive data breach affecting nearly 200 companies, including cybersecurity leaders Jamf, HackerOne, and LastPass, after hackers exploit a lingering credential left active since 2022.
- July – August 2026: Iranian-linked actors step up attacks against U.S. water and energy providers, with the Cybersecurity and Infrastructure Security Agency (CISA) confirming over 100 water systems targeted in July alone. The ATF confirms its own major incident via a ransomware group. In August, medical device manufacturer Boston Scientific suffers a global operational shutdown lasting weeks. Australian police arrest two suspects tied to the TeamPCP supply chain hacks.
- September 2026: A catastrophic breach at identity document verification service IDScan exposes a dark-web search engine containing the driver’s licenses and personal photos of 150 million North Americans, sparking immediate federal probes.
Supporting Data: The Scale of the Damage
The sheer volume of compromised records and affected populations in 2026 underscores the systemic nature of these attacks:
- 150 Million: The estimated number of U.S. and Canadian driver’s licenses exposed in the dark-web leak originating from IDScan.
- 30 Million: Students and faculty members whose private records were compromised during the ShinyHunters intrusion into Instructure’s Canvas system.
- 15 Million & 9.5 Million: The staggering number of healthcare records compromised in the DentaQuest insurance breach and the Aesto Health billing software incident, respectively.
- 100+: The number of U.S. water systems targeted by Iranian-linked actors during the summer months, disproportionately affecting underfunded municipal and private utility providers.
- Tens of Thousands: High-profile Instagram accounts hijacked via Meta’s AI chatbot logic flaw before the vulnerability was patched.
Official Responses and Regulatory Reckoning
As the boundaries between corporate negligence and national security blur, governments and regulatory bodies have scrambled to respond, though critics argue the interventions are lagging far behind the sophistication of the threat actors.

The Federal Response and Whistleblower Disclosures
In the United States, disclosures to Congress have become routine under mandatory reporting thresholds for "major cyber incidents." The FBI and ATF congressional notifications marked rare public acknowledgements of foreign intelligence penetrations into sensitive law enforcement apparatuses.
Concurrently, explosive whistleblower testimony regarding the Department of Government Efficiency (DOGE) and its sweeping, unregulated access to federal databases—specifically the Social Security Administration—ignited fierce bipartisan condemnation. House Democrats characterized the potential exposure of living Americans’ Social Security numbers on unsecured third-party servers as "the largest data breach in our nation’s history," prompting ongoing federal litigation.
International Law Enforcement Action
Cross-border law enforcement has yielded occasional victories. The August arrests in Australia of two individuals linked to the TeamPCP supply chain attacks—which impacted OpenAI, Mercor, and European cyber agencies—demonstrated the efficacy of international task forces. However, law enforcement remains severely hammed by the decentralized, state-sanctioned nature of groups operating out of non-extradition jurisdictions.
Implications: The Fracturing of Digital Trust
The cumulative weight of 2026’s cyber incidents points toward profound long-term consequences for global society, corporate governance, and individual privacy.

The Death of Digital Identity Verification
Perhaps the most alarming implication of the 2026 breaches is the collapse of reliable digital identity verification. With hundreds of millions of passports, driver’s licenses, and biometric records circulating on dark-web forums—highlighted by the IDScan disaster—the foundational premise of "Know Your Customer" protocols and emerging government-mandated age-verification laws is fundamentally broken.
When stolen credentials can easily bypass digital checks, online platforms and closed communities can no longer verify identities with any degree of certainty. As security researchers have repeatedly demonstrated, identity-checking systems now present a honeyed trap: centralized repositories of highly sensitive data that inevitably become targets for catastrophic breaches.
Critical Infrastructure as the New Frontline
The targeted disruption of water treatment plants in Poland and the United States, alongside attacks on European energy grids and medical device manufacturers like Stryker and Boston Scientific, signals a dangerous doctrine of total warfare. Critical infrastructure providers—particularly privately-held or municipal entities operating on legacy codebases with restricted budgets—are structurally ill-equipped to withstand sophisticated nation-state campaigns. The shift from mere espionage to active, destructive sabotage of physical infrastructure threatens to convert everyday civilian life into collateral damage in geopolitical conflicts.
The Corporate Risk Equation
For corporations, 2026 has exposed the dangerous friction between rapid AI adoption and foundational cybersecurity hygiene. Whether it is Klue relying on a four-year-old dormant credential, or Hasbro suffering weeks of paralyzing operational downtime, companies are learning that aggressive cost-cutting and digital transformation strategies without commensurate security hardening carry existential financial risks.

As insurance premiums skyrocket, regulatory penalties mount, and ransomware extortionists continue to exploit supply chain linkages, organizations can no longer treat cybersecurity as an afterthought. In the sobering reality of 2026, security is business continuity—and without it, the digital foundation upon which modern society rests threatens to give way entirely.
