
By Christopher Jones
Solutions Architect at Woo
Main Facts: The Invisible Threat to Modern E-Commerce
When headlines announce that major brands like The North Face have suffered a customer account breach, the digital retail community pauses for a moment before moving on with the workday. Typically, these incidents are imagined as cinematic, high-stakes events: a dramatic website blackout, a flashing ransom demand, or a team of elite hackers aggressively bypassing firewalls.
In reality, most modern e-commerce breaches are shockingly quiet. Attackers rarely need to smash digital windows when they can simply walk through the front door using stolen login credentials—a technique known as credential stuffing.
For the average online store owner, this raises a deeply unsettling question: If a similar attack targeted your platform today, how would you find out? Would a specialized security tool raise an immediate red flag? Would your internal team notice aberrant customer behavior? Or would your first warning come from an angry customer filing a support ticket or, worse, a public relations disaster?
In the fast-paced ecosystem of digital retail, accountability is often heavily fractured. Customer support teams monitor incoming tickets, operations manage daily fulfillment and orders, and third-party agencies keep an eye on site uptime. Within this siloed structure, a malicious card-testing run or a coordinated stuffing attack looks like harmless background noise—a few scattered support queries here, a slight bump in failed payment notifications there, and absolute silence on the uptime monitoring chart.
It is only when an analyst views all three data streams simultaneously that the pattern reveals itself as an active cyberattack. Unfortunately, most e-commerce operations lack a unified dashboard or a designated individual positioned to connect these dots in real-time.
Chronology: The Lifecycle of an Unnoticed E-Commerce Breach
Understanding how a security compromise unfolds over time is critical to intercepting threats before they cause irreparable damage to revenue and brand reputation. While every cyber incident is unique, successful breaches generally follow a predictable chronological arc.
Phase 1: Reconnaissance and Baseline Probing
Long before any malicious code is executed or accounts are accessed, bad actors map out their targets. They analyze the platform architecture, test checkout endpoints for vulnerabilities, and probe login pages for weaknesses. During this phase, automated bots may launch low-volume card-testing attacks. On a busy store, a dozen failed micro-transactions blend seamlessly into daily operations, leaving traditional monitoring tools entirely blind to the preliminary assault.
Phase 2: Credential Stuffing and Account Compromise
Armed with data dumps harvested from unrelated third-party data breaches, attackers deploy automated scripts to test millions of username and password combinations against your customer database. Because these attempts mimic legitimate human login behavior—often utilizing distributed proxy networks to mask IP addresses—they bypass basic rate-limiting firewalls. Once a handful of accounts are successfully breached, attackers pivot to exploiting saved payment methods, loyalty points, or stored personal identifiable information (PII).
Phase 3: Lateral Movement and Privilege Escalation
Once inside the ecosystem, sophisticated attackers do not merely stop at customer accounts. They may scan the WordPress or WooCommerce dashboard for outdated plugins, unpatched vulnerabilities, or misconfigured administrative user roles. By escalating their privileges from a standard customer account to an administrator, malicious actors can inject malicious JavaScript (such as digital skimming or Magecart malware) directly into the checkout pipeline to siphon credit card data from unsuspecting buyers.
Phase 4: Operational Disruption and Monetization
In the final stages, attackers extract their value. This can range from bulk purchasing high-value digital goods using stored credit cards to exfiltrating customer databases for sale on dark web marketplaces. At this stage, oddities begin to multiply: sudden spikes in chargebacks, abnormal refund requests, and an influx of password-reset complaints from legitimate users who find themselves locked out of their accounts.
Phase 5: Detection and Public Fallout
For stores lacking centralized logging and real-time behavioral analytics, this is the moment of truth. Detection rarely happens because of an automated security alert; instead, it occurs reactively. Customers flood social media channels or support queues complaining of unauthorized orders. Only now does the merchant realize a breach has occurred, thrusting them into a frantic race for containment, forensic investigation, and mandatory regulatory reporting.
Supporting Data: Establishing Your Operational Baseline
Preventing this cascade of events requires abandoning a reactive posture in favor of proactive baseline awareness. The most critical first step in digital security is understanding precisely what constitutes "normal" behavior for your specific store. Without a clearly defined baseline, recognizing an anomaly is practically impossible.
Store owners and technical leads should regularly audit and document core operational metrics. At a minimum, teams should evaluate:
- Average Daily Order Volume: Knowing your standard transaction count highlights unexpected transaction spikes or sudden drops.
- Typical Refund and Chargeback Rates: Sudden fluctuations in reversed transactions often point directly to fraudulent purchasing activity.
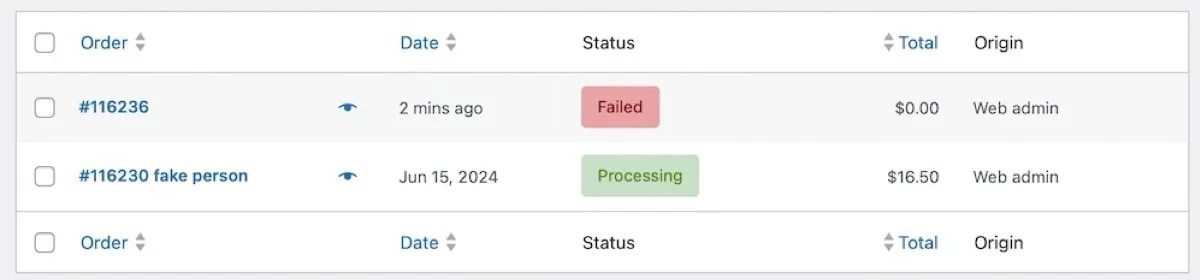
- Failed Order Frequency: A sudden surge in declined payments is a classic indicator of automated card-testing bots.
- Average Order Value (AOV): Significant deviations can signal that bad actors are testing specific price thresholds or unloading high-value inventories.
- Inventory and User Accounts: A thorough accounting of all active administrator accounts and installed plugins ensures unauthorized backdoor entries are spotted instantly.
Deep Dive: Where to Look Within the WordPress and WooCommerce Dashboard
Even for large-scale operations, the standard WordPress dashboard yields invaluable forensic clues. While these indicators do not definitively prove a hack on their own, they provide essential context when evaluated alongside broader site activity.
+-----------------------------------------------------------------+
|                    DASHBOARD FORENSIC CHECKLIST                 |
+-----------------------------------------------------------------+
| [ ] WooCommerce Analytics -> Orders  (Look for unusual spikes)  |
| [ ] Order History                    (Inspect failed payments)  |
| [ ] WordPress Users Section          (Audit admin accounts)     |
| [ ] System Status / Error Logs       (Check for anomalies)      |
+-----------------------------------------------------------------+
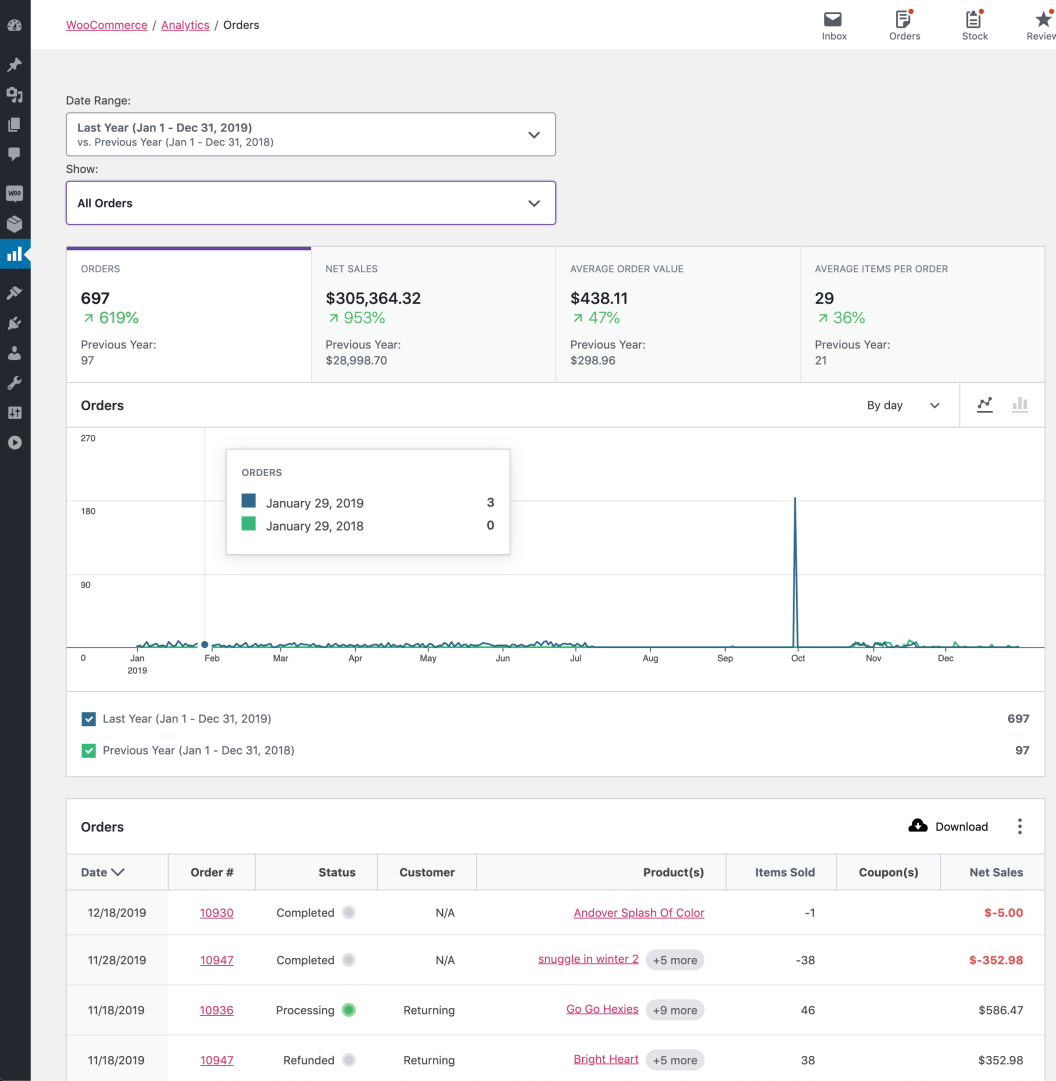
1. WooCommerce Analytics
Navigating to Analytics → Orders within your WordPress dashboard establishes your quantitative baseline. Watch closely for uncharacteristic order surges originating from narrow geographic regions, unusual purchasing hours, or repetitive cart configurations.
2. Order History and Failed Transactions
Your order history is frequently the earliest harbinger of trouble. Keep a vigilant eye on orders marked as "Failed" or "Pending." A sudden accumulation of failed transactions accompanied by identical billing details or rapidly cycling credit card numbers strongly suggests an automated botnet is running card-testing scripts against your payment gateway.
3. User Accounts and Privilege Audits
Regularly inspect the Users section of your WordPress dashboard. Ask yourself: Who has administrative access to your store, and what actions are they authorized to take? Unrecognized administrator accounts, newly created user profiles with elevated privileges, or accounts tied to unfamiliar email addresses are critical red flags demanding immediate investigation.
Official Responses and Enterprise Solutions
While the native WordPress dashboard provides necessary visibility, it does not inherently diagnose complex hacking attempts or sophisticated security breaches. To achieve a comprehensive security posture, merchants must deploy third-party tools specifically engineered to connect disparate data points and issue instant alerts when anomalies arise.
Jetpack Security and Activity Logging
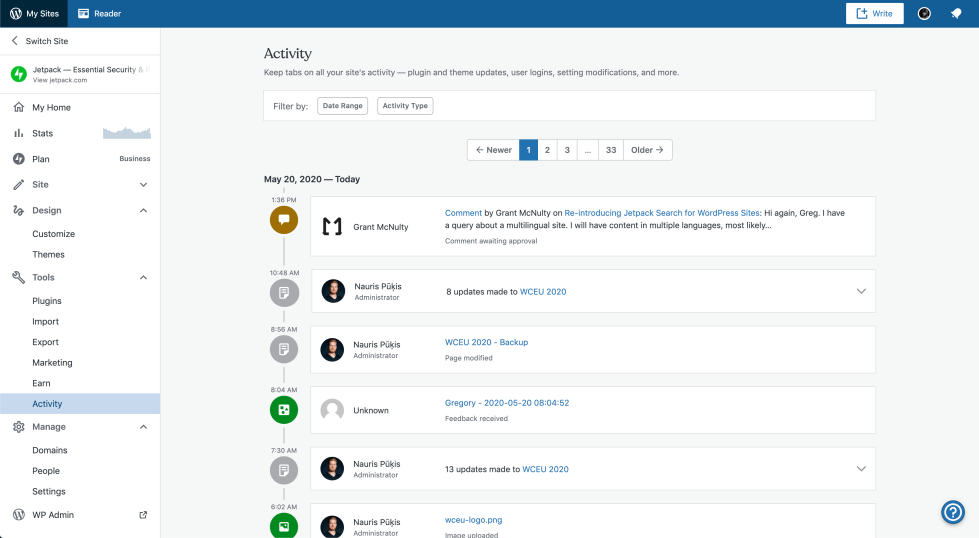
Industry standards recommend implementing solutions like Jetpack Security, which delivers real-time security alerts coupled with an exhaustive, immutable activity log. This grants administrators granular, actionable visibility into every single event, file modification, and login attempt occurring across the site.
Anti-Fraud Shields for WooCommerce
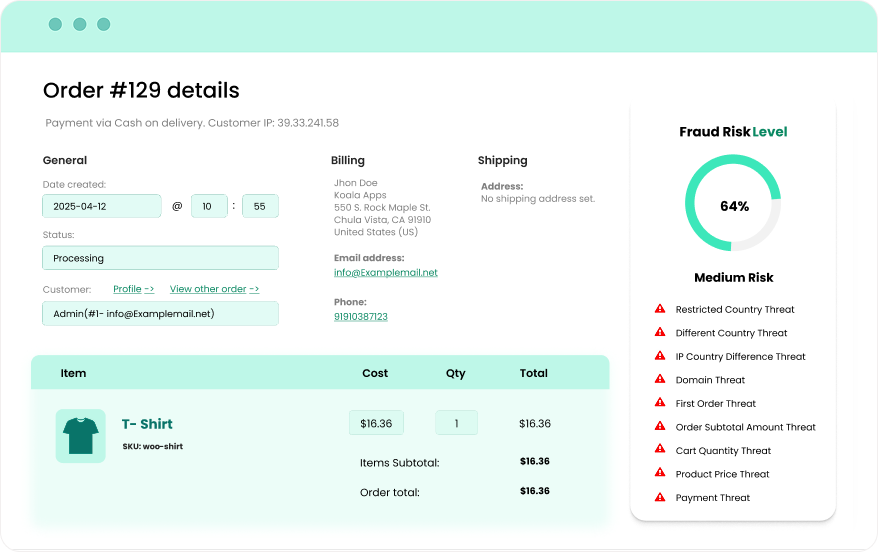
Payment gateways such as WooPayments and Stripe feature built-in fraud prevention systems (like Stripe Radar). However, high-volume merchants often benefit from dedicated extensions like Anti-Fraud Shield for WooCommerce. These tools evaluate secondary risk factors—such as device fingerprinting, proxy detection, and velocity checks—to flag high-risk orders and alert teams before fulfillment takes place.
Enterprise Observability with Datadog
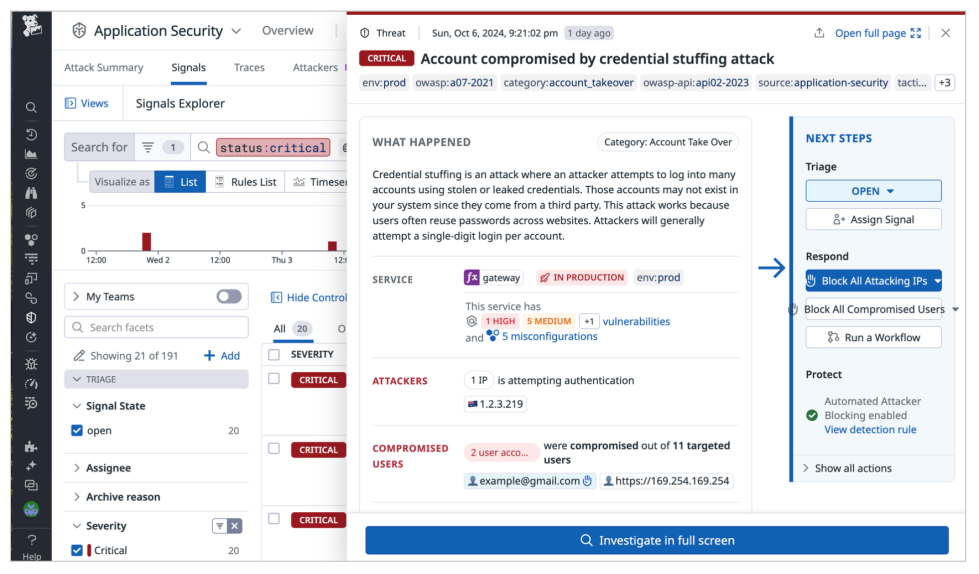
For multi-channel merchants operating complex retail infrastructures, platforms like Datadog offer centralized application monitoring. By aggregating logs and metrics from your WooCommerce store, payment processors, and hosting environments into a single dashboard, Datadog extends security visibility far beyond the traditional WordPress backend.
Furthermore, leading managed hosting providers actively monitor server-level vulnerabilities, scanning for injected malware and alerting site administrators to structural anomalies directly within the hosting control panel. When these disconnected systems are integrated into a unified monitoring strategy, security teams can detect anomalous patterns earlier, identify root causes instantly, and neutralize threats before they escalate into enterprise-level crises.
Implications: Building a Resilient Future
Securing an e-commerce platform is not a one-time project; it is an ongoing operational discipline. While deploying advanced logging, anti-fraud shields, and enterprise observability tools forms the backbone of a long-term security strategy, merchants must also institute immediate operational safeguards to minimize unnecessary risk:
- Enforce Mandatory Multi-Factor Authentication (MFA): Require MFA for all administrative and shop manager accounts to neutralize credential-stuffing attacks.
- Implement Strict Principle of Least Privilege: Regularly audit user roles to ensure team members and third-party agencies only possess the exact permissions required for their specific functions.
- Establish Rapid Incident Response Protocols: Ensure that support, operations, and technical teams have a designated communication channel to cross-reference anomalies immediately when suspicious activity is flagged.
- Maintain Aggressive Update Schedules: Keep WordPress core, WooCommerce, themes, and all installed plugins updated to patch known vulnerabilities before malicious actors can exploit them.
Security alerts matter immensely, but they do not always manifest as flashing sirens or dramatic system failures. More often than not, the earliest indicators of a breach are subtle shifts in order volumes, user account creations, or payment gateway failures. The ultimate key to safeguarding your digital storefront lies not just in the strength of your firewall, but in your team’s ability to recognize those subtle changes and respond with decisive speed.
