
By Christopher Jones, Solutions Architect at Woo
When major retail brands like The North Face fall victim to credential stuffing attacks and customer account breaches, the news cycle inevitably focuses on the scale of the compromise. Headlines flash across our screens, corporate PR teams issue damage-control statements, and security analysts dissect the forensic details of how malicious actors managed to bypass the perimeter.
For the average e-commerce merchant scrolling through their morning news feed, these stories often feel distant. They read like corporate problems reserved for multinational conglomerates with dedicated, around-the-clock cybersecurity operations centers.
Yet, the uncomfortable truth of modern digital retail is that automated credential stuffing, card-testing rings, and low-level intrusion attempts target stores of all sizes. When an attack hits a mid-sized or growing WooCommerce store, there is rarely a dramatic website outage, a flashing red alarm, or an explicit ransom note left on the homepage. Instead, attackers quietly leverage stolen login credentials to test customer accounts, siphon loyalty points, or probe checkout gateways.
If a similar incident were to unfold on your digital storefront tonight, how would you find out? Would an advanced security tool flag the anomaly in real-time? Would your team spot the subtle behavioral shifts in day-to-order metrics? Or would your first definitive warning come from an angry customer service email or a social media complaint?
For many online merchants, the terrifying answer is the latter. This article examines the hidden anatomy of e-commerce security breaches, maps out the structural blind spots that allow attacks to slip through the cracks, and provides a blueprint for establishing proactive, multi-layered detection strategies.
The Anatomy of Modern E-Commerce Blind Spots
To understand why security breaches frequently catch store owners off guard, one must look closely at how modern e-commerce organizations operate. In most mid-sized retail operations, departmental silos are deeply entrenched.
- Customer Support monitors ticketing systems, managing returns, password resets, and shipping complaints.
- Operations and Logistics keep a close eye on incoming orders, fulfillment bottlenecks, and inventory levels.
- External Agencies or IT Partners monitor server uptime, core software updates, and basic database health.
When automated threat actors launch a card-testing run or a coordinated credential stuffing campaign, the indicators do not arrive wrapped in a neat, alarming package. To an isolated department, the signs look entirely like background noise: a slight uptick in failed payment gateway responses, three or four unusual support tickets about locked accounts, and zero impact on the uptime charts.
An attack only reveals its true form when an observer has the vantage point to connect all three data streams at once. Unfortunately, in the vast majority of e-commerce businesses, no one is positioned—or equipped—to bridge these operational silos.
Establishing Your Baseline: The Foundation of Threat Detection
The most critical step in safeguarding an e-commerce store is not installing the most expensive enterprise firewall on the market; it is establishing a comprehensive understanding of what constitutes normal behavior for your specific digital ecosystem. Without a baseline, anomaly detection is impossible.
Store owners and operations managers must regularly audit and document core operational metrics to recognize when something deviates from the norm. Sit down with your management, development, and support teams to map out:
- Average Daily Order Volume: What is your typical transaction count across weekdays versus weekends?
- Typical Refund and Chargeback Rates: What percentage of daily revenue is normally reversed or disputed?
- Failed Order Frequency: How many checkouts fail daily due to declined credit cards or technical glitches?
- Average Order Value (AOV): Are transaction sizes holding steady, or are there sudden, unexplained spikes in high-ticket purchases?
- Inventory & Plugin Inventories: What third-party plugins are currently active, and exactly which user accounts possess administrative privileges?
Even for large-scale operations, the WordPress and WooCommerce dashboards provide profound clues to potential security incidents. You simply need to know how to interpret the data.
Mining the WordPress and WooCommerce Dashboards for Clues
While default dashboards do not explicitly shout "Hacking Attempt!" when a breach occurs, they capture the digital footprints left by malicious actors. Most warning signs must be interpreted within the broader context of your site’s day-to-day traffic.
1. WooCommerce Analytics
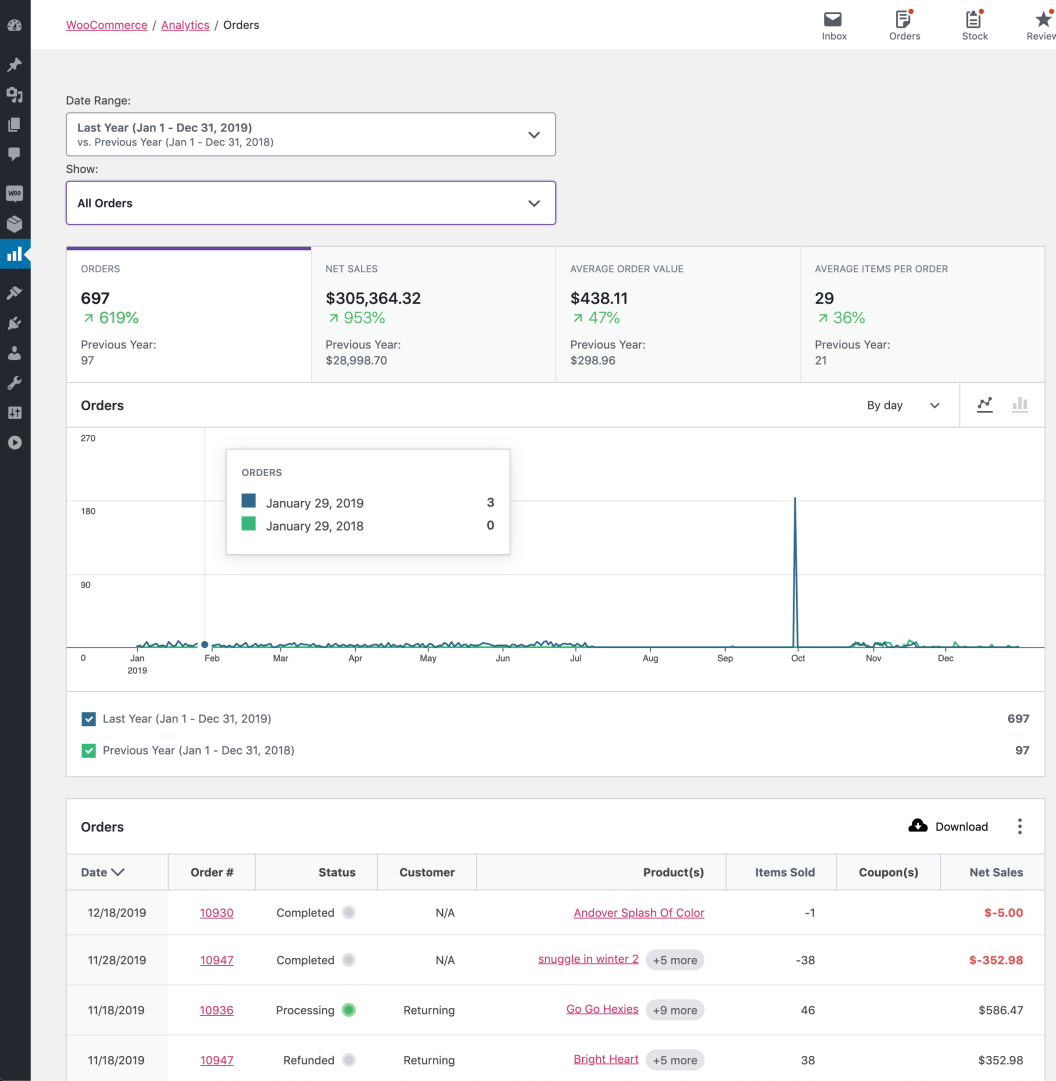
Your primary baseline lives within the Analytics → Orders screen of your WordPress dashboard. Regular review of this section helps identify anomalies such as:
- Sudden, unseasonal spikes in transaction volume originating from concentrated geographic locations.
- Uncharacteristic surges in low-value orders, which often indicate automated bots testing stolen credit card combinations (card testing).
- Rapid shifts in preferred payment gateways during specific, off-peak hours.
2. Order History and Payment Failures
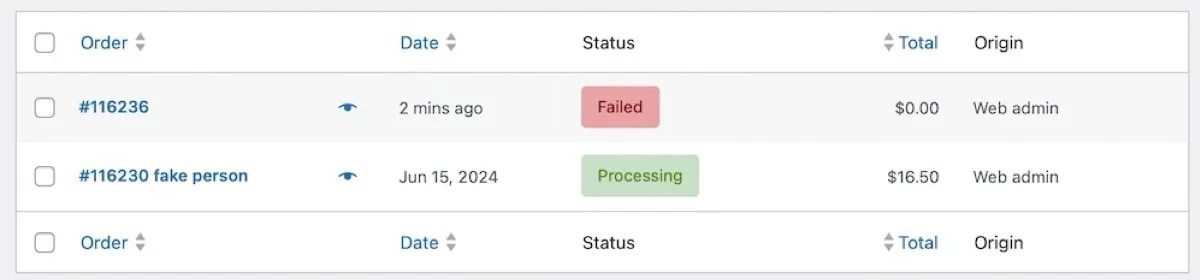
A sudden influx of failed orders is one of the most reliable indicators of card testing or automated checkout abuse. Pay close attention to:
- Clusters of orders failing instantly due to Address Verification System (AVS) mismatches or CVV rejections.
- Multiple failed transactions executed in rapid succession using identical IP addresses or customer billing profiles.
Pro Tip: Modern payment gateways like WooPayments and Stripe feature built-in machine-learning fraud protection tools. If you utilize a different payment processor, investigate how they handle fraud screening and collaborate with your development team to tighten risk-tolerance rules.
3. User Accounts and Privilege Escalation
Unauthorized access often begins with compromised administrative or shop-manager credentials. Periodically audit the Users section of your WordPress dashboard to verify:
- The creation of unexpected administrator or editor accounts, particularly those created outside of standard working hours.
- Accounts with elevated privileges that have not logged in for extended periods.
- Changes to user email addresses or password reset requests originating from unfamiliar administrative endpoints.
4. Additional Dashboard Indicators
Beyond orders and users, keep a watchful eye on auxiliary indicators of compromise:
- Unfamiliar plugins appearing in your plugin directory or core files being modified without a corresponding deployment ticket from your development agency.
- Sudden spikes in database query loads or unexpected outbound network requests logged by your hosting provider.
Chronology of an Attack: From Silent Probe to Public Disclosure
Understanding how a breach evolves helps illustrate why relying solely on reactive measures is a failing strategy.
- Phase 1: Reconnaissance and Credential Stuffing (Days 1–3)
Botnets leverage lists of credentials leaked from unrelated data breaches across the web, automatically testing them against your customer login portal. Because these attempts mimic legitimate human login requests, standard web application firewalls (WAFs) may not trigger an alert. - Phase 2: Abuse and Monetization (Days 4–7)
Once inside valid accounts, attackers may exploit stored credit card tokens, purchase digital goods, or execute card-testing scripts. Failed payments begin to trickle upward, while low-level customer complaints regarding locked accounts or altered profile information land in support queues. - Phase 3: Operational Fragmentation (Day 8)
The store continues operating normally on uptime monitors. Customer service fields isolated tickets; operations sees minor payment friction. The disconnect prevents internal teams from recognizing an active security incident. - Phase 4: External Discovery or Public Disclosure (Day 14+)
Either an observant security tool finally flags an anomaly, or customers begin posting on social media about unauthorized charges. The store is forced into reactive damage control, public relations management, and expensive forensic investigations.
Supporting Data and Industry Context
The threat landscape facing e-commerce platforms is expanding in both volume and sophistication. According to recent cybersecurity benchmarks:
- Credential Stuffing Efficiency: Automated bot attacks account for up to 40% of all web traffic on retail sites during peak shopping seasons, with credential abuse being the primary vector for unauthorized account access.
- The Cost of Silence: Studies show that businesses that detect and contain security breaches within the first 30 days save an average of $1 million in remediation costs, regulatory fines, and brand equity loss compared to those where breaches linger undetected.
- The Human Element: Over 80% of security incidents involving content management systems like WordPress stem from compromised credentials, outdated plugins, or unpatched vulnerabilities rather than zero-day software exploits.
Official Responses and Industry Best Practices
Leading security frameworks and e-commerce platform architects emphasize a shift away from perimeter-only security toward Defense-in-Depth.
When major brands experience breaches, official post-incident reports nearly always highlight the same foundational failures: lack of centralized logging, absence of multi-factor authentication (MFA) enforcement for administrative users, and delayed detection timelines.
To bridge the gap between basic dashboard monitoring and enterprise-grade security posture, merchants must deploy dedicated cross-channel tooling that connects disparate data points.
Essential Tooling for Comprehensive Store Visibility
While the WordPress dashboard provides vital clues, third-party integrations are required to connect the dots and deliver instant notifications before small issues snowball into catastrophic breaches.
1. Jetpack Security
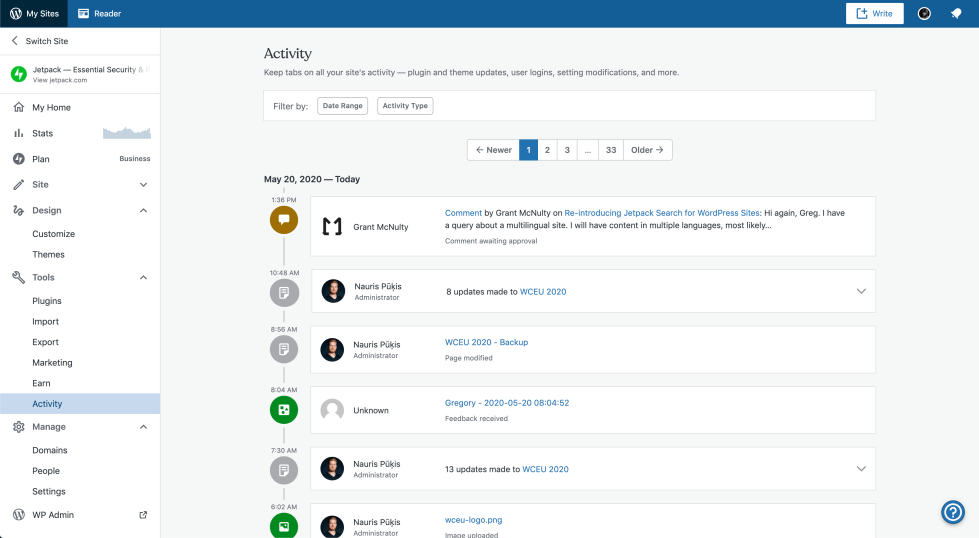
Start by implementing Jetpack Security, which offers real-time security alerts, automated malware scanning, and a comprehensive activity log. The activity log provides granular, chronological visibility into every single action that takes place on your site—from plugin updates and file edits to user logins and order modifications.
2. Anti-fraud Shield for WooCommerce
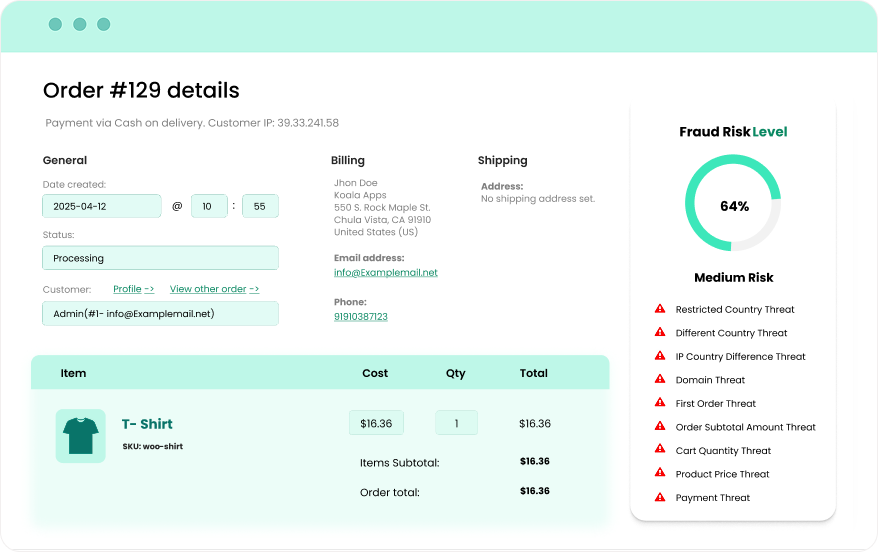
To combat sophisticated payment fraud and card-testing rings, integrate specialized tools like Anti-fraud Shield for WooCommerce. This solution goes beyond basic payment gateway fraud protection by analyzing deep behavioral signals, assigning risk scores to incoming orders, and alerting your team based on customized risk thresholds.
3. Datadog (For Multichannel Retailers)
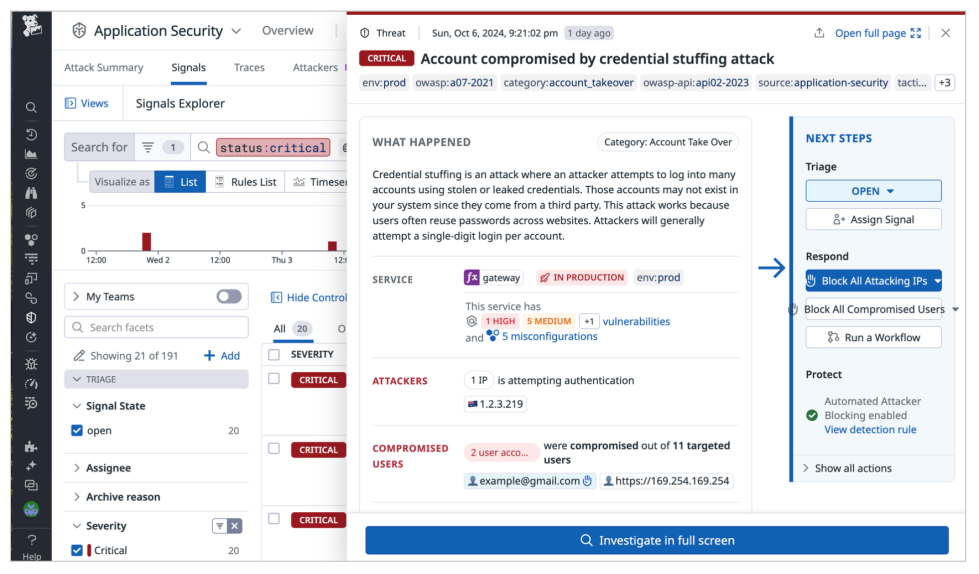
For growing brands operating across multiple sales channels (e.g., WooCommerce, mobile apps, and brick-and-mortar POS systems), Datadog provides robust application performance and security monitoring. By centralizing security telemetry into a single dashboard, Datadog extends your visibility far beyond the boundaries of your WordPress environment.
4. Hosting-Level Vulnerability Scans
Never underestimate your hosting provider. Many specialized WooCommerce hosts track site vulnerabilities, malware signatures, and anomalous server behavior directly within the hosting control panel, pushing instant alerts when server-level files are compromised.

Immediate Steps to Reduce Risk Today
While architectural overhauls and security strategies take time to plan and execute, merchants can take decisive, immediate action today to dramatically reduce their attack surface:
- Enforce Strong Authentication: Require complex passwords and mandate Multi-Factor Authentication (MFA) for all administrative, editor, and shop-manager user accounts.
- Audit User Roles: Immediately remove inactive administrative accounts and downgrade user roles to the principle of least privilege.
- Update Everything: Ensure WordPress core, your active theme, and all installed plugins are running their most up-to-date, patched versions.
- Review Payment Gateway Settings: Enable advanced fraud filtering (such as strict AVS and CVV checks) directly within your payment processor settings.
- Establish an Incident Response Protocol: Ensure your support, operations, and technical teams know precisely who to contact if an unusual cluster of customer complaints or payment failures arises.
Conclusion
Security alerts and automated firewalls are indispensable, but they do not always tell the whole story. The earliest indicators of a sophisticated e-commerce breach rarely arrive as flashing sirens; instead, they manifest as subtle, seemingly disconnected shifts in order velocity, account activity, and payment friction.
By understanding your store’s baseline, consolidating your monitoring data, and responding swiftly to minor anomalies, you can transform your e-commerce platform from a soft target into a resilient, highly defended digital storefront.
