
By Christopher Jones
Solutions Architect at Woo
Main Facts: The Anatomy of a Modern E-Commerce Breach
When headlines announce that a major brand like The North Face has suffered a customer account breach, the public usually imagines a cinematic cyberattack: a high-tech siege, flashing red server rooms, massive website outages, or extortionate ransom demands flashing across a monitor.
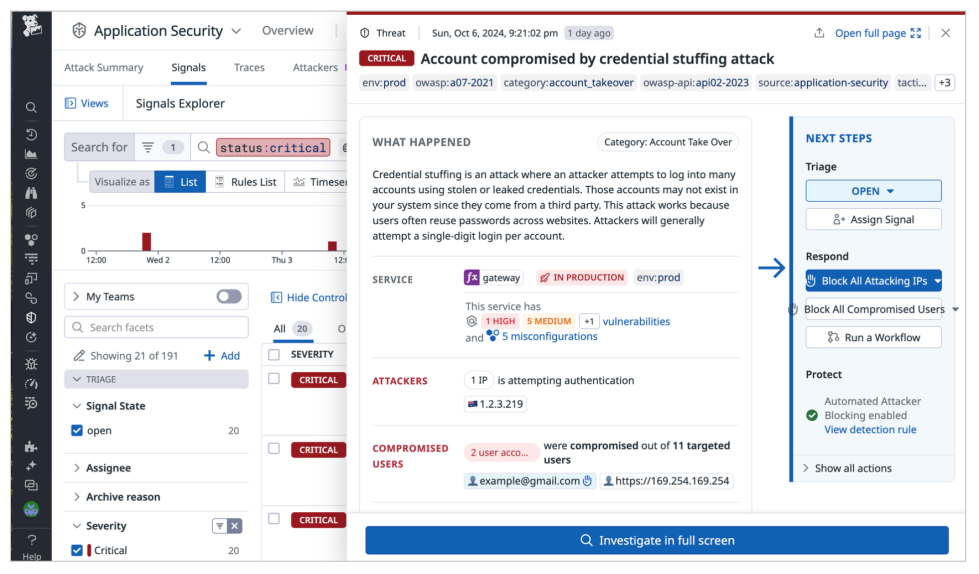
In reality, most modern e-commerce security breaches look entirely ordinary on the surface. They do not announce themselves with downtime or dramatic system failures. Instead, malicious actors frequently rely on credential-stuffing attacks—utilizing username and password combinations stolen from entirely unrelated data leaks—to quietly slip into customer accounts.
For online merchants, this reality raises an uncomfortable question: If your store were quietly breached tomorrow, how would you find out?
Would a dedicated security tool alert you immediately? Would your team spot the subtle anomalies before escalation? Or would your first warning arrive via an irate customer who noticed unauthorized charges or locked-out accounts?
In most organizations, information is siloed. Customer support monitors help tickets, operations watches daily fulfillment orders, and an external agency tracks server uptime. Within this fragmented structure, malicious behaviors—such as a coordinated card-testing run—resemble harmless background noise. A few odd support tickets here, a slight bump in failed payment notifications there, and zero blips on the uptime chart.
It is only when someone correlates all three data streams simultaneously that the pattern reveals an active attack. Unfortunately, in the vast majority of e-commerce setups, no single person or tool is positioned to see the whole picture.
Chronology: The Lifecycle of an Undetected Store Compromise
Understanding how an exploit unfolds over time is critical for merchant defense. Breaches rarely happen in a single, isolated moment; they follow a stealthy, multi-stage evolution.
Phase 1: Reconnaissance and Baseline Probing
Before launching a full-scale attack, malicious scripts or bad actors quietly probe an e-commerce site. They test checkout endpoints, scan for outdated plugins, and check the responsiveness of login pages. At this stage, the activity mimics standard automated web traffic or curious shoppers, blending seamlessly into daily analytics.
Phase 2: Credential Stuffing and Automated Testing
Once vulnerabilities or weak points are identified, bad actors deploy automated scripts to test millions of stolen credential pairs against the store’s login portal. Simultaneously, they may initiate low-value card-testing runs—charging tiny amounts to stolen credit cards to verify which numbers are still active.
During this phase, customer support might field a slight uptick in password-reset inquiries, while payment gateways register a minor spike in failed transactions. Because these symptoms affect different departments, they are rarely flagged as a unified security threat.
Phase 3: Lateral Movement and Privilege Escalation
If an attacker successfully compromises a customer account—or worse, an administrative account—they begin moving laterally. They might harvest stored customer data, alter shipping addresses on pending orders, inject malicious JavaScript to skim checkout data, or create backdoor admin users to ensure persistent access even if primary credentials are reset.
Phase 4: Discovery and Fallout
For unmonitored stores, this phase is triggered reactively. Customers report fraudulent orders, credit card companies issue chargeback warnings, or payment processors freeze merchant accounts due to suspicious activity. At this point, the business shifts into crisis management, dealing with public relations fallout, regulatory reporting, and costly forensic investigations.
Establishing the Baseline: Knowing Your Store’s Normal Rhythm
The single most effective defense against sophisticated, quiet breaches is an intimate understanding of baseline operations. You cannot spot an anomaly if you do not know what normal looks like.
Store owners and development teams must actively document their operational metrics. Sit down with your team this week and formally record:
- Average daily order volume and peak purchasing hours.
- Typical refund and chargeback rates.
- Baseline ratios of failed-to-successful orders.
- Average order value (AOV).
- The precise inventory of installed plugins, themes, and admin-level user accounts currently active on the site.
Even for high-volume stores, the WordPress and WooCommerce dashboards provide invaluable clues to potential problems. However, interpreting these clues requires contextual awareness. No single data point guarantees a security breach on its own; they must be evaluated within the broader ecosystem of your site’s daily activity.
Supporting Data and Dashboard Diagnostics: What to Look For
To catch anomalies before they escalate into catastrophic breaches, merchants must routinely inspect key areas of their e-commerce architecture.
[Store Activity] ──> [Siloed Departments] ──> [Disconnected Signals] ──> [Delayed Detection]
                             │
                             └──> [Unified Dashboards / Jetpack / Anti-Fraud] ──> [Real-Time Defense]
1. WooCommerce Analytics
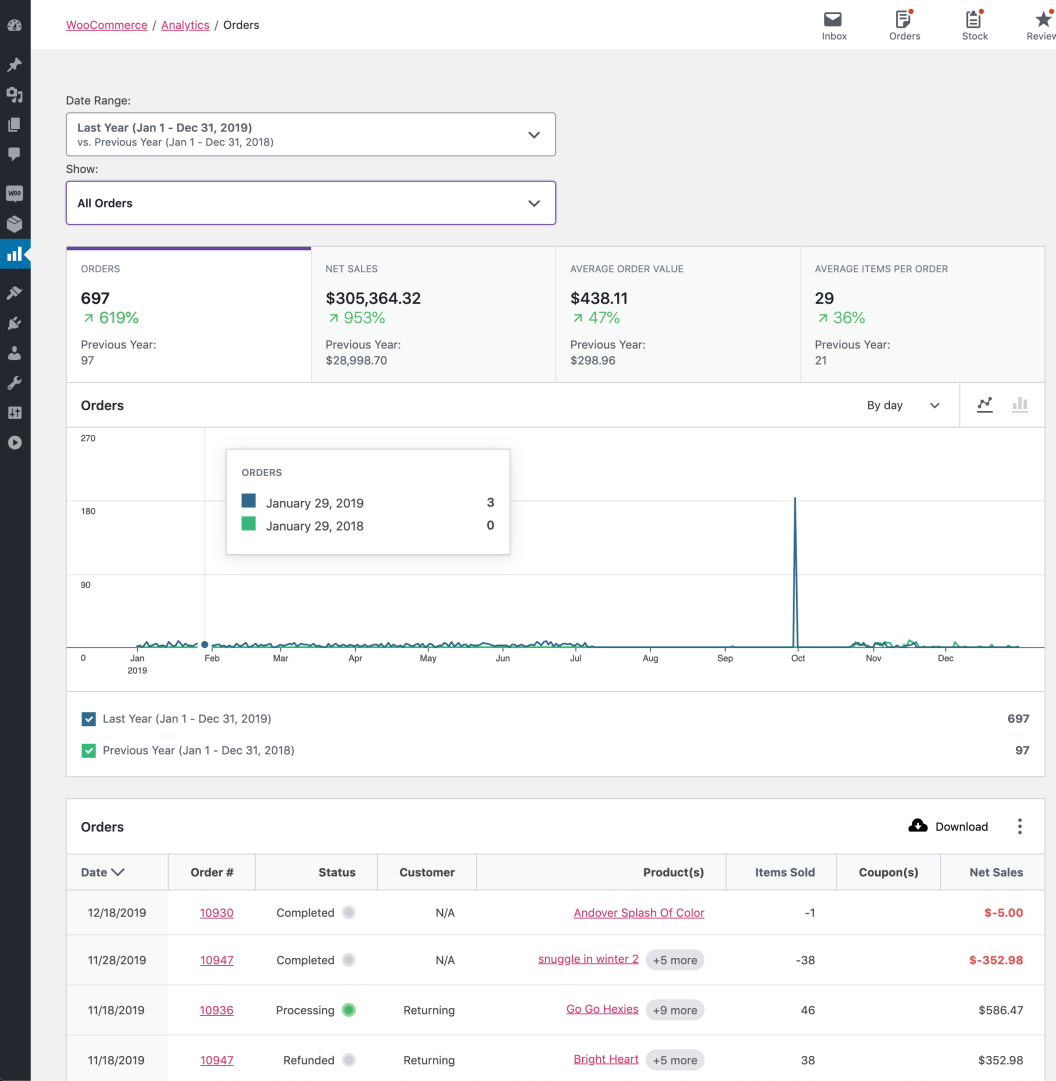
Navigate to Analytics → Orders in your WordPress dashboard to monitor baseline trends. Look out for sudden, unexplained spikes in order volume originating from unusual geographic locations, or clustering of orders just beneath your free-shipping threshold, which often points to automated testing scripts.
2. Order History and Failed Transactions
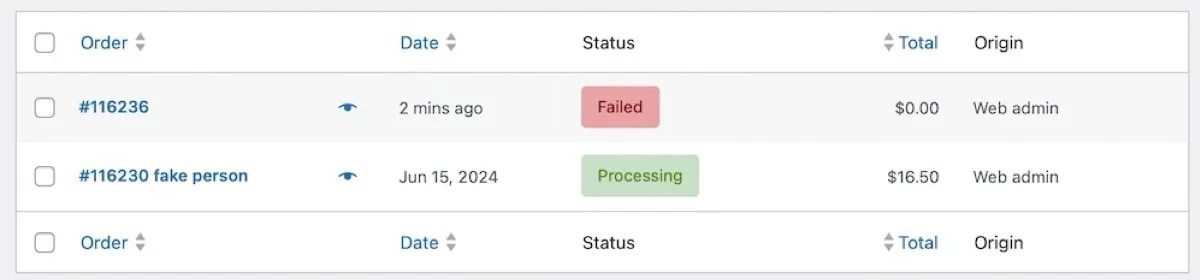
Your transaction logs are often the canary in the coal mine. Keep a close eye on:
- Clusters of failed checkout attempts using varying credit card details from the same IP address.
- Sudden increases in orders that are immediately canceled or refunded.
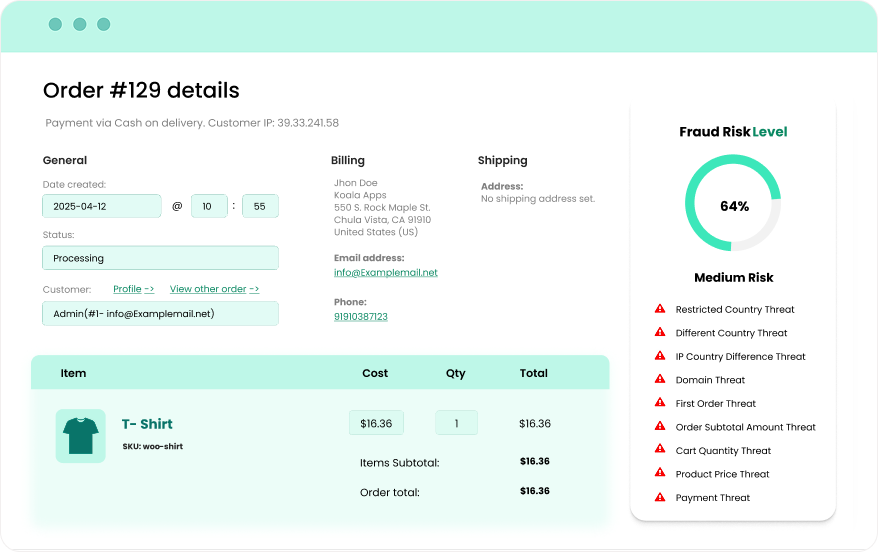
- Orders where the billing and shipping countries drastically mismatch without logical justification.
Pro Tip: Modern payment gateways like WooPayments and Stripe feature robust, built-in fraud protection mechanisms. If you utilize a different payment gateway, review its fraud settings immediately and collaborate with your development team to tighten security rules.
3. User Accounts and Role Management
Regularly audit the Users section of your WordPress dashboard. Review who holds administrative privileges and verify their recent actions. Watch for:
- Unfamiliar accounts with administrator or shop manager capabilities.
- Accounts created outside of standard business hours or without an associated customer support ticket.
- Sudden modifications to user email addresses or permission levels.
Beyond user roles, audit your site’s file modification dates, error logs, and plugin directories. Unauthorized changes to core files or newly installed plugins you do not recognize are glaring red flags.
Official Responses and Enterprise Solutions
While the WordPress dashboard offers essential visibility, it does not natively provide enterprise-grade, real-time threat intelligence or automated intrusion detection. To bridge this gap, merchants must deploy interconnected monitoring tools that aggregate signals across multiple channels.
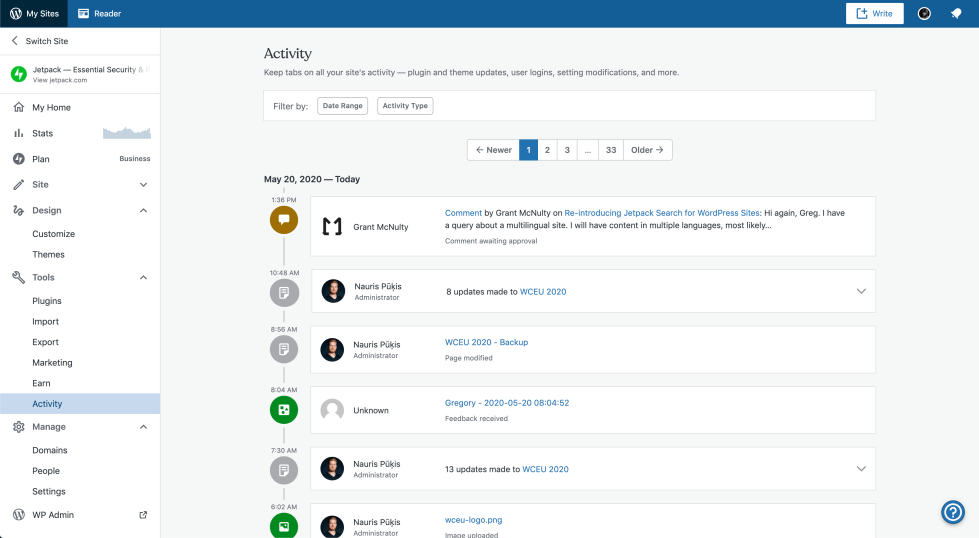
Real-Time Activity Monitoring with Jetpack Security
Implementing tools like Jetpack Security provides instant security alerts and maintains a granular, immutable activity log. This grants merchants actionable visibility into every single event occurring on their site—from plugin updates and file modifications to user logins—ensuring teams are notified the moment something deviates from the norm.
Advanced Risk Scoring with Anti-Fraud Shields
Basic payment gateway filters are often insufficient against targeted attacks. Integrating specialized solutions like Anti-Fraud Shield for WooCommerce adds a critical layer of defense. These tools analyze order risk factors based on custom-configured thresholds, automatically flagging high-risk transactions and alerting your team before fulfillment occurs.
Centralized Observability with Datadog
For multi-channel merchants operating stores across various platforms alongside WooCommerce, enterprise monitoring solutions like Datadog offer centralized visibility. By consolidating security logs, application performance data, and infrastructure metrics into a single dashboard, Datadog extends a security team’s monitoring perimeter far beyond the traditional WordPress admin panel.
Furthermore, premium hosting providers frequently incorporate automated malware scanners and vulnerability notification systems directly into their hosting dashboards, giving merchants an additional early-warning system against emerging threats.
Implications for E-Commerce Strategy
Integrating these monitoring systems shifts an organization’s security posture from reactive firefighting to proactive defense. When your security tools, payment gateways, activity logs, and hosting alerts are connected, your team can detect unusual patterns earlier, isolate the root cause faster, and neutralize threats before small vulnerabilities snowball into headline-making breaches.

While building a comprehensive, multi-layered e-commerce security strategy requires careful planning and resource allocation, merchants can take immediate, actionable steps today to minimize unnecessary risk:
- Enforce Strict Authentication Policies: Mandate strong, unique passwords and enforce Multi-Factor Authentication (MFA) for all administrative and shop manager accounts.
- Minimize Attack Surfaces: Immediately uninstall inactive plugins, unused themes, and abandoned user accounts that could serve as backdoors for attackers.
- Audit Access Permissions: Review user roles to ensure the principle of least privilege is applied—no team member should have higher permissions than their daily workflow requires.
- Keep Everything Updated: Establish a rigorous, automated schedule for updating WordPress core, themes, and plugins to patch known security vulnerabilities promptly.
- Establish Incident Response Protocols: Ensure your team knows precisely who to contact, what data to preserve, and how to communicate with customers if suspicious activity is detected.
Security alerts matter immensely, but they rarely present themselves with blaring sirens and flashing lights. The earliest indicators of a compromise are almost always subtle shifts in order flows, account creations, or site activity. By learning to recognize these micro-changes and responding with swift, coordinated defense, merchants can protect their revenue, safeguard their customers’ trust, and secure the long-term health of their business.
